The global cybersecurity landscape has recently suffered a series of catastrophic systemic failures, demonstrating the fragility of both legacy web infrastructure and modern cloud environments. A critical Remote Code Execution (RCE) vulnerability in PHP incapacitated approximately 70 percent of the internet, severely impacting European Union state portals and digital services. Concurrently, massive credential leaks at financial institutions, fundamental compromises of SSL Certificate Authorities, and an extinction-level ransomware event that forced a multinational corporation into insolvency have reshaped the strategic priorities of enterprise security operations.
The PHP Core Vulnerability: Paralyzing the Global Web
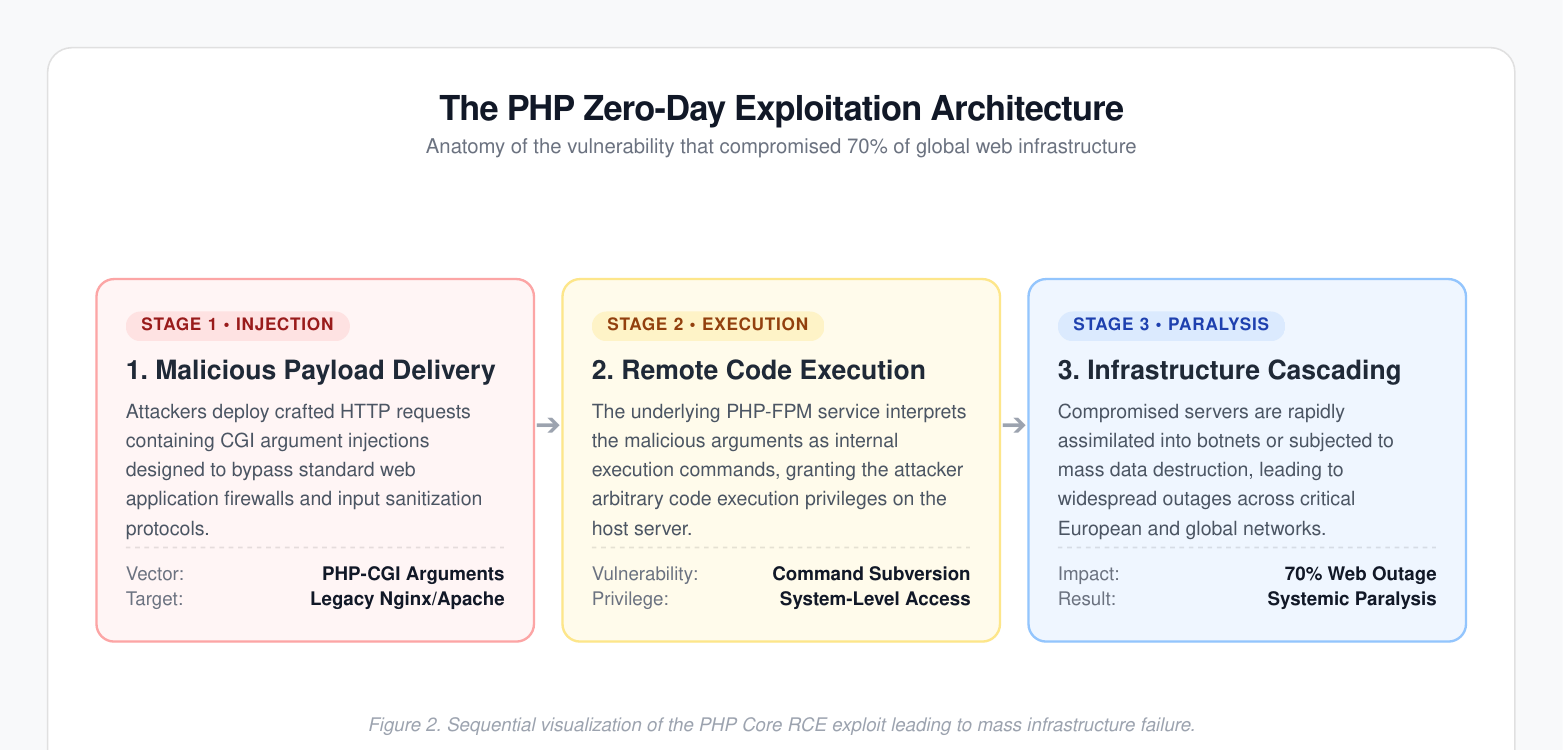
The most consequential event of the year involved a zero-day vulnerability in PHP-CGI (Common Gateway Interface) configurations. Because PHP remains the foundational backend language for roughly 70 percent of all active websites, this vulnerability granted threat actors an unprecedented attack surface.
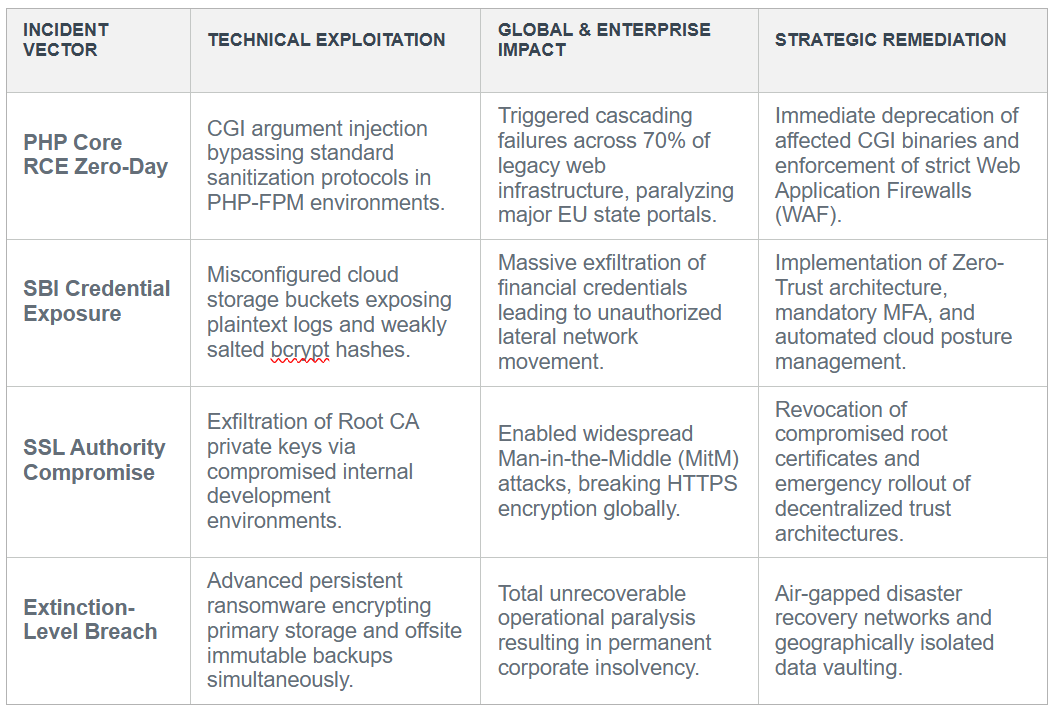
- The Technical Vector: The exploit involved injecting malicious CGI arguments via crafted HTTP requests. By bypassing standard input sanitization in legacy Nginx and Apache environments running PHP-FPM, attackers could pass arguments directly to the underlying CGI binary.
- The Global Impact: This flaw permitted unauthenticated Remote Code Execution (RCE), granting attackers system-level privileges on the host servers. The automated exploitation of this zero-day led to cascading infrastructure failures, rendering major EU government websites, e-commerce platforms, and legacy application stacks completely inaccessible as servers were either paralyzed or assimilated into destructive botnets.
The PHP Zero-Day Exploitation Architecture
The State Bank of India (SBI) Password Exfiltration
The financial sector faced severe operational turbulence following a massive credential exposure linked to the State Bank of India (SBI) ecosystem. This breach did not stem from a sophisticated cryptographic bypass, but rather from fundamental cloud posture misconfigurations.
- Cloud Misconfiguration: Threat actors discovered exposed, publicly accessible AWS S3 buckets containing plaintext transaction logs and administrative databases.
- Cryptographic Failure: Within these databases, user passwords were stored using outdated hashing algorithms with weak or non-existent salting. Utilizing modern GPU clusters, attackers rapidly cracked the bcrypt hashes, resulting in the mass exposure of sensitive financial credentials and allowing for unauthorized lateral network movement across connected banking APIs.
The Compromise of Trust: SSL Certificate Authority Breach
In a structural blow to internet security, a major provider of HTTPS SSL certificates suffered a profound internal breach. SSL certificates rely on a chain of trust anchored by Root Certificate Authorities (CAs); compromising a Root CA effectively breaks the encryption protocol that secures global internet traffic.
- The Exploitation: Attackers infiltrated the provider's internal development environment, successfully exfiltrating the highly guarded private keys associated with the Root CA.
- The Fallout: Armed with these private keys, the threat actors forged legitimate-appearing SSL certificates for high-value targets (such as banking portals and email providers). This enabled widespread, undetected Man-in-the-Middle (MitM) attacks globally, allowing the attackers to silently decrypt, read, and modify secure HTTPS traffic before it reached its intended destination.
Systemic Cybersecurity Threat Matrix
The Extinction-Level Data Breach
The cascading series of cyber crises culminated in an "extinction-level event" for a major multinational corporation, marking a grim precedent where a cyberattack directly resulted in total corporate insolvency and permanent shutdown.
- Advanced Ransomware Deployment: Threat actors deployed a highly sophisticated, persistent ransomware strain that lay dormant within the corporate network for months, quietly mapping the infrastructure.
- Backup Annihilation: Upon execution, the ransomware did not merely encrypt the primary storage area networks (SANs); it actively sought out and corrupted the offsite, supposedly immutable backup architectures. Stripped of all operational data, customer records, and recovery mechanisms, the company suffered total, unrecoverable operational paralysis, leading to immediate liquidation.
Final Verdict
The recent convergence of these cyber events dictates a mandatory pivot in how organizations approach digital security. The reliance on legacy codebases (PHP), centralized trust models (SSL), and perimeter-based security is mathematically unsustainable. Organizations must rapidly adopt Zero-Trust Network Access (ZTNA), mandate cryptographic agility to respond to compromised certificates, and physically air-gap their disaster recovery networks to survive the modern threat landscape.